Blog
Notes from inside the tenancy.
Detection engineering, incident response and Microsoft security — written by the analysts doing the work, not a marketing team.
Security operations · Jul 2026
AI and humans in a modern SOC: Who should do what?
From alert triage and detection engineering to incident response and client communication, not every security task should be handed to AI. We examine the roles AI and humans should play in a modern SOC.
Read the post →
Risk and compliance · Jul 2026
ISO 27001 certification, and why it’s a big deal
Security maturity isn’t a badge. It’s the ongoing discipline of governance, risk management and continuous improvement.
Security operations · Jun 2026
Tales from the SOC: Real-world AI use in cyber
AI isn’t coming for cyber. It’s already here. And both attackers and defenders are using it to move faster, scale harder, and lower the barrier to entry. Here’s what that actually looks like from the SOC.
Threat intelligence · May 2026
Cyberattacks are rising. Does staying safe have to cost more?
As cyberattacks continue skyrocketing alongside global unrest, many organisations are rethinking their approach. Here’s why MDR is becoming a critical part of staying protected.
Threat intelligence · Apr 2026
We did say Iran would ‘stryke’ while the iron’s hot. And they did.
Predicted cyber retaliation has materialised following escalating tensions involving Iran. A hacktivist attack on global medical company Stryker highlights the real‑world impact of geopolitics on cyber risk.
Incident response · Aug 2025
Where Passion and Capability Intersect – Decrypting an Infostealer
Infostealer malware remains a major threat. Tarian Cyber’s senior team reversed and decrypted an attempted attack, transforming findings into same-day detection engineering for stronger client protection.
Security operations · Aug 2025
A Timely Reminder – Tools Do Not Replace Experience
For SMEs, cyber tools aren’t enough. True resilience comes from pairing technology with experienced analysts who can interpret threats, respond decisively, and protect business continuity.
Incident response · Aug 2025
Threat Report – ‘Lazarus’ APT targeting Australian technology sector
Lazarus Group targets Australia’s tech sector with fake recruiters and malicious repositories. Tarian Cyber’s incident response uncovers evolving tactics and reinforces the need for vigilant detection and threat intelligence.
Security operations · Aug 2025
The Simplistic Art of Targeted Detection Engineering
Tarian Cyber embeds detection ownership across its team – “you write it, you triage it” – enabling targeted, automated detection for high-impact threats while reducing noise and scaling efficiently via detection-as-code.
Security operations · Aug 2025
Your Geo-Blocking Policy Isn’t Enough Anymore
Geo-blocking and MFA are no longer enough. Threat actors exploit residential proxies and phishing domains – real-time detection and resilient SOC services are now critical.
Incident response · Aug 2025
Total Chaos – What happens when Aussie customers’ data is stolen?
Infostealer malware and underground markets turn stolen data into criminal profit. Tarian Cyber provides dark net intelligence to help organisations detect leaks, assess exposure, and strengthen resilience.
Security operations · Jul 2024
What is an adversary-in-the-middle attack?
Adversary-in-the-middle phishing bypasses MFA by stealing session cookies. Tarian Cyber equips organisations with detection, response, and phishing-resistant authentication to defend against this evolving threat.
Threat intelligence · Jun 2024
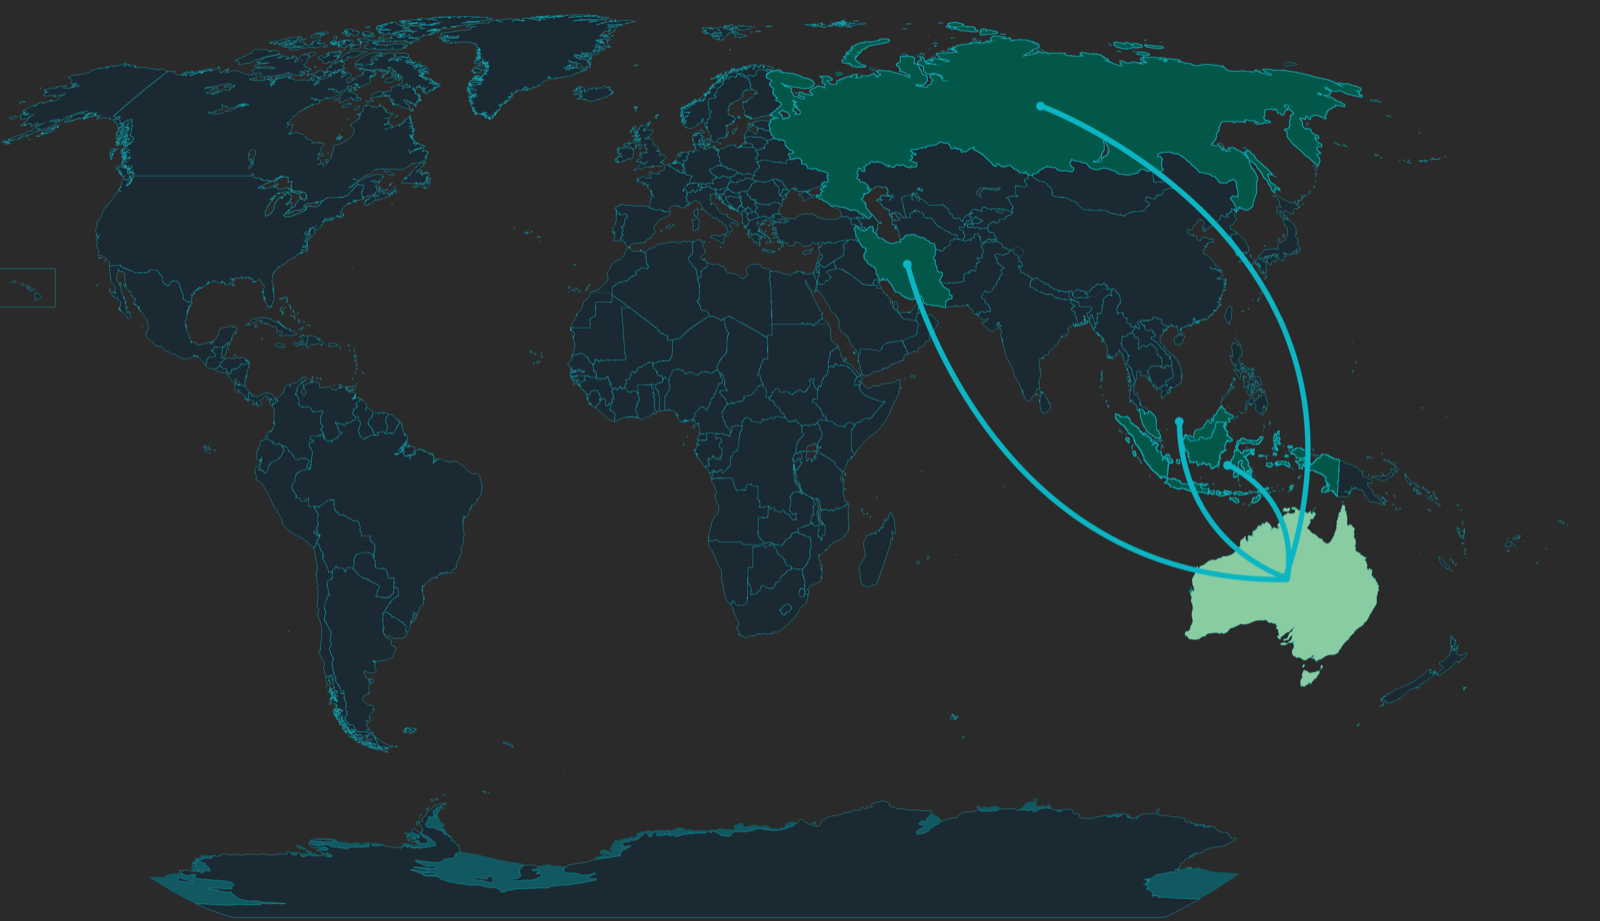
The rising capabilities of Hacktivist groups threatening Australia
Hacktivist groups are escalating attacks on Australia, moving from DDoS to breaches and misinformation. Tarian Cyber’s MDR integrates dark net monitoring and intelligence to strengthen resilience.
Security operations · Jun 2024
A new standard for a new era – SMB1001
Tarian Cyber has achieved SMB1001:Level 3 certification. For Australian SMBs, Silver or Gold is the right target. Our uplift package provides expert guidance and 24/7 support.
Endpoint security · Jun 2024
Multi-Factor Authentication – it is not your saviour (yet)
The most common incident we have responded to since the inception of Tarian Cyber, similar to most Incident Response firms, is Business Email Compromise (BEC).
Free insights for CISOs & IT leaders
The 5 Hard Truths About SOC Procurement in FY26
Hard questions every CISO, IT leader, and risk owner should be asking (and how to avoid the costly missteps most teams make).
Our certifications
Real People - Real Capability - Real Certifications
Ready to connect?
Ready to get on board with Tarian Cyber in as few as four hours?
Schedule a discovery call with Australia's Microsoft-native cyber security specialists. Learn how we can strengthen your security posture while maximising your existing investments.